
Server authority
Validation authority remains server-side for protected interaction decisions.
Security
ColorShield ID validates authorized form interactions before protected submissions continue, with continuous monitoring, centralized visibility and AuditGuard evidence.
Security model
Validation authority remains server-side for protected interaction decisions.

Authorized domains and protected flows are evaluated as part of interaction context.

Session context contributes to whether the current interaction remains trusted.

Form identity distinguishes the protected interaction type and expected context.

A time-bound authenticity proof is issued for validated interactions.

When validation cannot confirm trust, policy can stop unsafe continuation.

Copied HTML/CSS/JS does not automatically reproduce an authorized validation context.

Visibility across critical form environments during protected sessions.
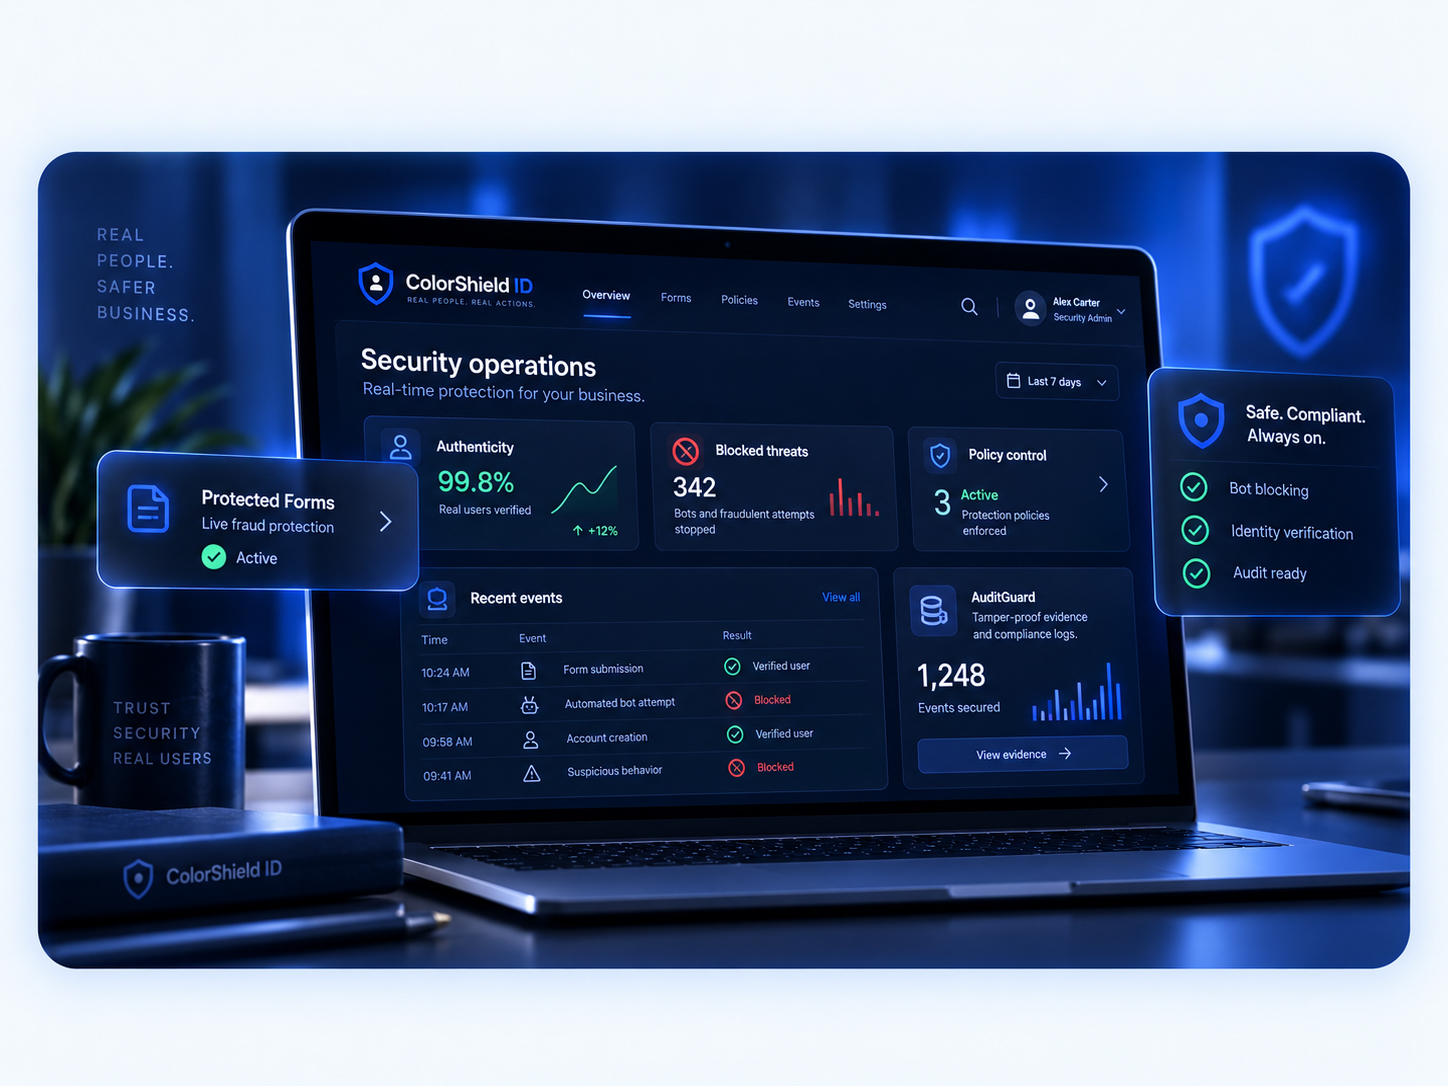
Security Operations
Security Operations provides Centralized Visibility across multiple domains, multiple flows, multiple environments and multiple locations, including login, checkout, payment and sensitive forms.
Conceptual topology for centralized visibility across protected login, checkout, payment and sensitive-data forms. Not live customer infrastructure.
Architecture visualization. Conceptual illustration for ColorShield ID Security Operations. Not a live customer map.
Attack classes
Select an attack class to see how ColorShield ID evaluates interaction context rather than appearance alone.
Attackers can reproduce the appearance of login or payment forms on unauthorized pages. ColorShield ID does not rely only on visual similarity. It validates the interaction context before treating the form as trusted.
Unauthorized changes to the page structure may alter the interaction while preserving much of the visible interface. ColorShield ID monitors the protected interaction context and validation state rather than trusting appearance alone.
Continuous monitoring and in-session interaction monitoring help identify unexpected changes during protected sessions.
Injected fields can attempt to collect sensitive information without replacing the entire page. ColorShield ID protection should communicate that the expected form identity and protected interaction matter, not only the surrounding website.
Interaction validation and form identity remain the deciding factors before the customer backend accepts a protected submission.
Users may be redirected or moved into an unauthorized interaction while believing they remain in the expected workflow. ColorShield ID validates protected interaction context before submission is accepted.
Others react after exposure. ColorShield validates before protected submission.
Module
AuditGuard is the evidence and enforcement-recording module for protected interactions. It is separate from Security Operations visibility.
Hard Block ModeBlock unsafe continuation when policy requires it.
 Warn & Record Mode
Warn while preserving evidence of the event.
Warning evidenceCapture context around warned interactions.
 Continuation evidence
Record when activity continues after a warning.
Audit trailRetain an operational trail of outcomes.
 Authorized notifications
Alert approved operators for critical events.